Sting Software
Pre-Obligation Risk Prevention
Sting stops it before it happens.
Most tools tell you what has already happened.
Sting operates before obligation, intercepting risk at the exact moment it would legally or financially bind your organization.
Employees don’t intentionally create risk. They sign up for tools, agree to terms, enter company credit cards, upload data to AI chatbots, and book demos — often without realizing they’ve created legal, financial, or compliance obligations.
Traditional tools only discover the problem after the damage is done. Sting captures it at the moment of intent.
Sting is the product of collaborative efforts with procurement and IT security professionals. Built with the Rust programming language, along with 18 months of iterative testing and thoughtful algorithm design, you can rest assured that Sting is secure, reliable, and runs entirely on your premises. With 94% recall (low missed alarms) and 99% precision (low false alarms), you get effective mitigation and lasting reconditioning of stakeholder behavior.
A product of Nield Consulting Group, based in Plano, Texas. Founded by Thomas Nield, technology architect, author, and AI safety advocate, Sting is a browser-based, on-premises solution that flags unauthorized procurement activity in real time: clickwrap agreements, e-signatures, credit card usage, and unauthorized downloads.
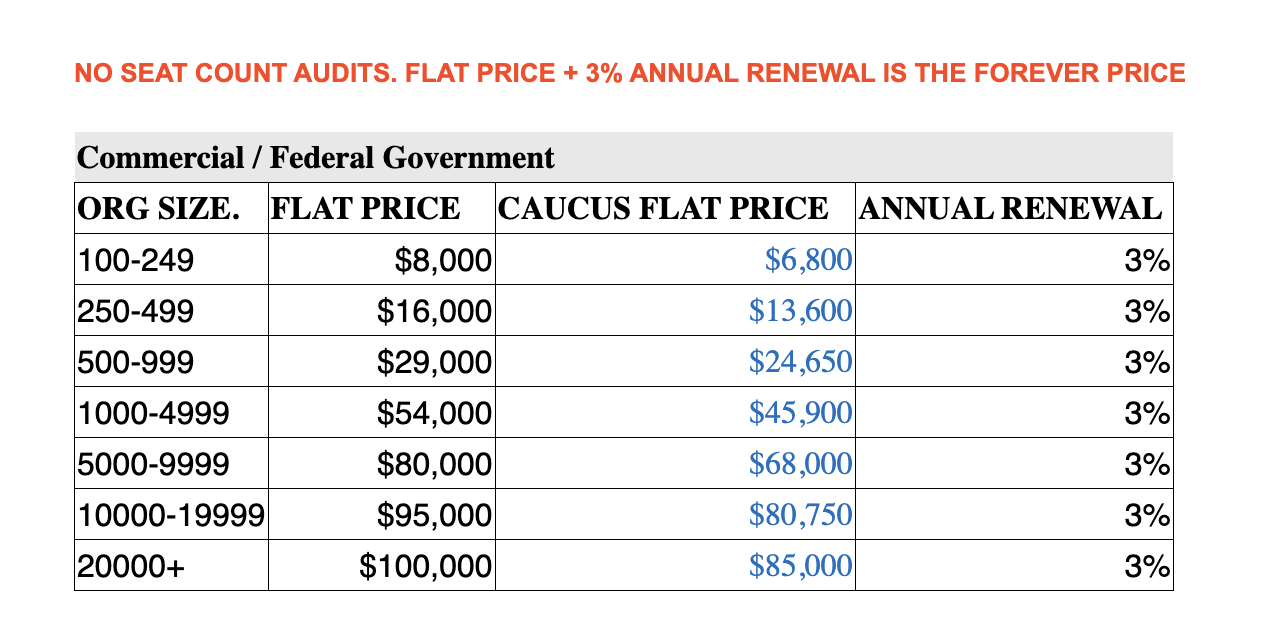
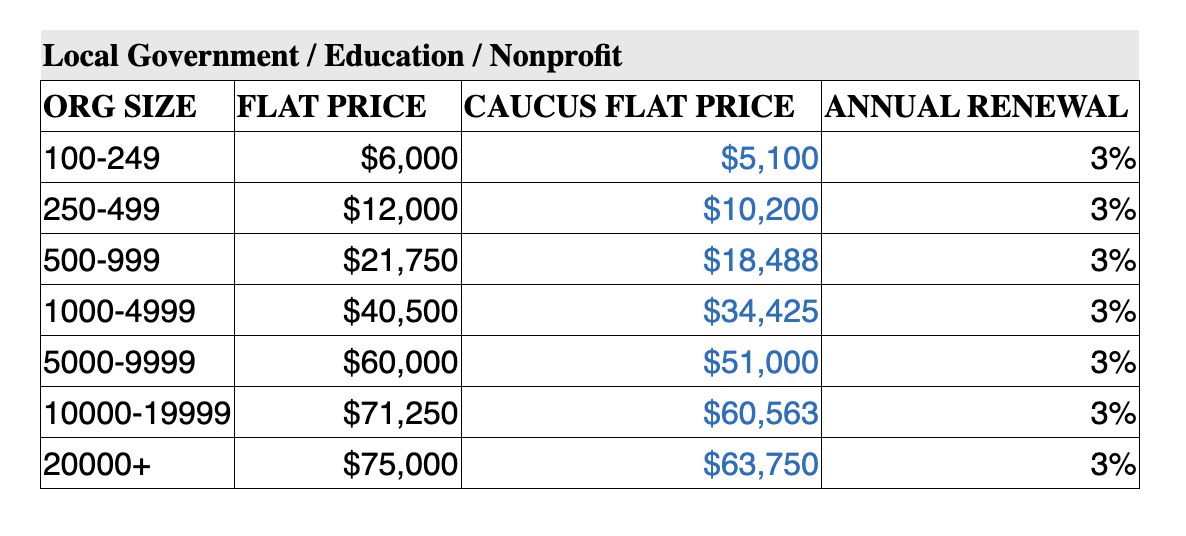
One annual license, unlimited users.